
Through our comprehensive courses, you’ll reskill, upskill, and supercharge your expertise, gaining a competitive edge in the evolving financial landscape. Led by industry experts, our hands-on sessions will equip you with the knowledge and tools to tackle financial challenges, drive innovation, and safeguard your organization.
The course is designed by Industry Experts having years of domain knowledge and are training on the subjects to multilateral agencies. A Perfect blend of academia with practical approach.
Why join our programs?
- Supercharge your finance career with cutting-edge skills
- Reskill & upskill for the AI-powered future of finance
- Bridge the gap between theory and practice through interactive sessions
- Applicable learning for CXOs, managers, and working professionals
- Network with peers and professionals across the industry
- Build job-ready skills in forensic accounting, AI, AML/CFT, analytics, and cyber security
- Learn from industry experts with real-world experience
THREE-LEVEL PROGRAM OFFERING
High-level strategy sessions designed exclusively for top-tier executives and decision makers.
Comprehensive programs that combine two or more M-Grade modules, designed for an integrated understanding of critical topics for department heads and team leaders.
Standalone, in-depth coverage of courses focused on specific skill sets, designed for frontline professionals to pick and choose based on their individual needs.
A1: Masterclass – AI and Risk for CXOs – 1 Day
High-level overview of everything AI, including emerging technologies from ChatGPT to Agentic AI and their strategic impact on organizational operations.
B1: Bootcamp – AI in Finance & Analytics – 3 Days
Deep dive into leveraging AI, ChatGPT, and advanced analytics for financial modeling, risk assessment, and strategic insights.
B2: Bootcamp – Cyber Security & Cloud Security – 3 Days
Comprehensive look at cyber threats, zero-trust architecture, cloud control matrices, and data protection frameworks.
B3: Bootcamp – Forensic Investigation & Analytics – 3 Days
Investigative techniques, data mining for fraud detection, and using AI-driven forensic tools in corporate investigations.
M1: Basecamp – AI in Finance & Accounting – 2 Days
Practical application of AI tools, automation of accounting processes, and real-time financial analysis.
M2: Basecamp – AI in Financial Reporting & Audit – 2 Days
Modernizing audit procedures with AI, predictive analytics for compliance, and automation in reporting.
M3: Basecamp Cyber Security – 2 Days
Fundamentals of cyber security, threat intelligence, incident response, and best practices for secure financial operations.
M4: Basecamp – Cloud Security, Cloud Control Matrix – 2Days
Cloud governance, risk assessment, and applying the Cloud Security Alliance (CSA) control matrix.
M5: Basecamp – Data Analytics & Wrangling for Finance – 2 Days
Data wrangling techniques, BI tools, and advanced analytics to drive financial decision-making.
M6: Basecamp – AML and Terror Financing – 2 Days
Key regulations, suspicious activity monitoring, and leveraging AI to detect and prevent illicit financial flows.
M7: Basecamp – Forensic Investigation – 2 Days
Investigation methodologies, digital evidence collection, and analysis in financial contexts.
M8: Basecamp – CFE Plus – 4 Days
Certified Fraud Examiner (CFE) course designed into a 4-day exam-oriented training for working professionals.
M9: Basecamp – CISA Plus – 4 Days
Certified Information Systems Auditor (CISA) training designed into a 4-day exam-oriented training for working professionals.
Outline
1 Day
AI & DIGITAL DISRUPTION IN FINANCE, RISK, AND GOVERNANCE
Strategic Perspective: AI as a Leadership Imperative
- Understanding the paradigm shift: AI, GenAI, and exponential tech in finance
- Why boardrooms need to be AIliterate
- CXO-level challenges: balancing disruption with governance
AI in Finance – What’s Real, What’s Hype
- Real-world transformations: predictive finance, risk scoring, AI-led forecasting
- Case studies: global finance and audit functions augmented by AI
- Questions CXOs should ask: adoption, accountability, and oversight
Governance, Ethics & Risk in AI Era
- Frameworks for AI governance and responsible deployment
- Regulatory lens: EU AI Act, SEBI, RBI perspectives
- Mitigating risks: bias, explainability, data integrity
CXO Roadmap: AI Strategy for the Enterprise
- Building AI-ready culture and teams
- Prioritizing use cases: where to invest and where to pause
- Interfacing with audit, compliance, and IT for scalable governance
- Strategy clinic: short exercises for identifying opportunity zones
3 Days
AI in Everyday Finance – Automate What Can Be Automated
AI Essentials for Finance Teams
- What is AI – simplified for finance professionals
- Why AI matters – cost, accuracy, turnaround
- Traditional vs GenAI – evolution and application in finance
Productivity with ChatGPT & Excel
- Generating finance policies, notes, and narratives using AI
- Excel + AI: Building intelligent formulas and macros without coding
- Workflow Simulation: ChatGPT to create, validate, and enhance real-time outputs
Accounts 2.0 – AI in Payables, Receivables & Close
- Streamlining bookkeeping using AI tools
- Real-world scenarios: Automating reconciliations, detecting mismatches
- RPA vs AI – where they work together in AP/AR
Analytics & Predictive Intelligence in Finance
Data Wrangling for Finance Teams
- Cleaning, organising, and structuring datasets for financial analysis
- Use of AI for anomaly detection and performance ratios
Predictive Insights & Forecasting
- Scenario-based modelling: cash flow, budgeting, forecasting
- What-if analysis using AI-based simulators
- Visualizing trends and outliers through dynamic dashboards
Interactive Hands-On
- Mapping an existing process for automation and analytics
- Building an AI-enabled dashboard for month-end reporting
Governance, Risk, Controls & Team Enablement
AI in Internal Controls & Compliance Monitoring
- Use cases – credit scoring, KYC triggers, anomaly detection
- Understanding where AI fits and where human oversight is essential
Ethics, Bias & Explainability
- How models make decisions – black box vs transparent AI
- Mitigating bias, hallucination, and data gaps
Adoption Strategy for Finance Teams
- Scaling AI from pilot to departmentwide use
- Enabling team readiness – documentation, SOPs, communication
- Change management essentials for AIled transformation
3 Days
Cybersecurity for Finance Professionals
Cyber Threats in the Finance Domain
- Why finance systems are a target: data, approvals, transactions
- Common attacks: phishing, ransomware, credential compromise
Identity, Access & Controls
- MFA, RBAC, and least privilege – what it means for finance teams
- Real examples: payroll system breach, compromised TDS filings
Incident Response Basics
- Detection, response, escalation – how mid-management responds
- Simulated drill: Email-based fraud & internal coordination
Cloud Security and Control Frameworks
Finance in the Cloud – Understanding Risk and Controls
- Shared responsibility model and key risks for finance apps
- Cloud Control Matrix – simplified explanation for non-tech users
- Common misconfigurations: examples from Tally, SAP, Zoho, cloud ERPs
Practical Security Controls
- Encryption, logging, geo-fencing, retention – practical deployment
- Finance-Specific Case: Backup failure and recovery response planning
Integrating Security into Governance, Risk & Compliance (GRC)
Security Embedded in Process, Not Just Policy
- IT governance and compliance expectations – RBI, SEBI, GDPR
- Audit-readiness: maintaining evidence, logs, and trails
Business Continuity and Disaster Recovery
- Defining RTO and RPO for critical finance processes
- Crisis management: internal and external stakeholder communication
Mid-Manager Roleplay
- Tabletop simulation: Data breach in payroll cloud system
- Risk evaluation, action plans, escalation mapping
3 Days
Foundational Concepts in Forensic Thinking
Forensic Investigation – Scope and Mindset
- Differentiating audit, investigation, and compliance roles
- Red flags – financial, behavioural, and structural
Fraud Typologies in Finance
- Embezzlement, payroll fraud, false invoicing, kickbacks
- New-age fraud: digital wallets, shell entities, digital lending platforms
Practical Case Analysis
- Mapping red flags in vendor payments using financial ratios and timelines
- Identifying indicators of layered fraud within ERPs
Conducting Investigations and Gathering Evidence
Structured Investigative Process
- From suspicion to scope – triage techniques and investigation planning
- Prioritising stakeholders, documentation, and time-sensitive leads
Evidence Collection – Financial, Digital & Verbal
- Email trails, ledger dumps, voice notes, chat logs, phone records
- Introduction to digital forensics: securing and imaging devices
- Chain of custody – practical walkthrough
Interviewing for Investigation
- Planning effective questioning
- Reading behavioural cues – what’s said and what’s not
- Common errors – leading, cornering, or disclosing too much
Reporting, Coordination & Resolution
Transaction Tracing
- Understanding layering and fund movement
- Practical tools for tracing – Excel + forensic logic
- Visual mapping of shell company transactions
Building Defensible Reports
- Forensic report structure – timeline, analysis, exhibits
- Tools for presenting complex data: fraud trees, flowcharts, maps
Interfacing with Authorities
- Role of the MLRO, internal counsel, statutory auditor
- Simulated walkthrough: Whistleblower alert to internal forensic action
2 Days
Foundational Concepts in Forensic Thinking
AI Simplified
- What is AI and why it matters
- Emerging roles, tools, and teams in finance
- Risks of ignoring AI in financial workflows
AI Use Cases in Finance
- ▪ Budgeting, forecasting, cash flow, treasury optimization
- Predictive finance for smarter decisions
- Automating repetitive tasks
ChatGPT, Excel & Finance Workflows
- Writing formulas, reports, and policies with ChatGPT
- Prompting for productivity in real finance scenarios
- Excel enhancements: AI formulas and no-code insights
Accounts 2.0 – AP, AR & Reconciliations
- AI for bookkeeping, reconciliation, and close cycle reduction
- RPA vs AI: dividing repetitive tasks
- Tools to streamline AP/AR Interactive Tool Demo
- Guided exploration of AI tools for accountants
- Mapping current workflows to identify automation opportunities
Ethical Finance in the AI Era
- Tackling bias, explainability, and hallucinations in AI
- Ethics checklist before deployment Scaling AI in Finance
- Adapting AI for small vs large teams
- Change management essentials
- AI integration roadmap & next steps
Conducting Investigations and Gathering Evidence
Credit, Compliance & Controls
- AI in credit scoring, compliance monitoring, and fraud detection
- Balancing AI with internal controls and human oversight
- Trust vs challenging AI outputs
AI-Ready Skills
- Future finance roles (model manager, finance automation lead)
- Prompt writing and model intuition for accountants
Ethical Finance in the AI Era
- Tackling bias, explainability, and hallucinations in AI
- Ethics checklist before deployment
Scaling AI in Finance
- Adapting AI for small vs large teams
- Change management essentials
- AI integration roadmap & next steps
2 Days
AI as the Future of Finance
- AI vs Traditional Tech: What’s Different and Why It Matters
- Real-World Cases of AI: From Trend Spotting to Fraud Detection
AI 101 for Finance
- Key AI Concepts Simplified: RPA, Machine Learning, GenAI, NLP
- Traditional AI vs GenAI: Changes in Reporting & Audit
- Understanding Algorithms Without Coding
GenAI Deep Dive
- GenAI (ChatGPT, DeepSeek, etc) for Finance and Accounting Teams
- Generating Reports, Automating Narratives, and Summarising Complex Data
- Managing GenAI Risks: Bias, Hallucinations, and Data Security
Smart Reporting
- Predictive Insights and Trend Forecasting in Financial Reports
- Real-Time Risk Monitoring and Anomaly Detection
- AI-Powered Dashboards: Beyond Static Reports
Audits in the Age of AI
- AI in Audit: Real-Time, Risk-Based, and Data-Driven
- AI-Powered Audit Platforms
- Internal Practices to Enable AI: Data, Workflows, People
Ethics and Governance
- AI Governance: Frameworks, Controls
- Ethical AI Use
AI Pitfalls in Reporting
- Top Mistakes When Adopting AI
- Regulatory Watch: EU AI Act, Global Compliance Trends
- How to Stay Audit-Ready in an AI World
Collaboration between Auditors & Finance Teams
- Auditors Expectation on AI Reporting
- Assurance vs AI Controls
- Building Synergy Between Internal and External Audit
2 Days
Cyber Awareness
- Cyber threats (phishing, malware, ransomware)
- Social engineering & why attackers target employees
- Key terms: firewalls, antivirus, encryption, zero trust
Systems & Risks
- Email, file sharing, video calls, collaboration tools
- Cloud platforms (Google Workspace, Microsoft 365, Slack)
- Work-from-home (WFH), BYOD, and new attack surfaces
- Digital fatigue & risky shortcuts (weak passwords)
Cyber Hygiene
- Strong passwords & MFA
- Safe handling of links, attachments, and updates
- Public Wi-Fi, USB, and personal devices
- Avoiding shadow IT
Compliance Basics
- Global frameworks (ISO 27001, NIST, SOC 2)
- Data classification & handling sensitive info
- Organizational cyber policies
- Secure use of portable storage, printers, portals
Access, Controls & Data Protection
- Least privilege & role-based access
- File sharing restrictions & secure data handling
- Data protection laws (GDPR, CCPA) basics
Recognizing & Responding to Threats
- Spotting suspicious emails, login alerts, fraud attempts
- Reporting phishing or breach suspicions
- Incident handling protocols & importance of swift action
Documentation & Shared Responsibility
- Logs, approval records, exception reports
- Simple recordkeeping for compliance & audits
- Collaborating with IT teams
- Aligning internal practices with external standards
2 Days
Cloud Basics for Business Users
- IaaS, PaaS, SaaS essentials
- Public, private, hybrid, multi-cloud models
- Shared responsibility model
Cloud Risks & Threats
- Data breaches, misconfiguration, shadow IT
- Unauthorized access, insecure APIs
- Business impact of cloud incidents
Introduction to Cloud Controls Matrix (CCM v4.0)
- Purpose and structure (17 domains, 197 controls)
- Key domains: data security, IAM, compliance, risk management
- CCM as a blueprint for secure cloud adoption
Deep Dive: High-Relevance Control Domains
- IAM, Security Incident Management, GRC, Application Security, Audit & Compliance
- Mapping controls to ISO 27001, SOC 2, GDPR, NIST
- Practical, non-technical explanations
Vendor Risk & Cloud Compliance
- Evaluating CSPs: SLAs, data residency, exit planning
- Third-party risk management & global regulations (GDPR, ISO, SOC 2)
- Cloud audit readiness & documentation
Implementing & Managing Cloud Controls
- Assigning responsibilities: IT, risk, legal, operations
- Data classification, encryption, user provisioning, access reviews
- Backup, recovery, and reporting expectations
Cloud Security Governance Essentials
- Policies vs. procedures for cloud security
- KPIs, internal audit checklists, escalation paths
- Incident response workflows & maintaining global standards
Applying the CCM in Practice
- Interpreting and adapting CCM controls
- Mapping controls to internal processes and responsibilities
- Continuous improvement for secure cloud operations
2 Days
Understanding Financial Data
- Importance of analytics in finance
- Descriptive, diagnostic, predictive analytics
- Structured vs. unstructured data
- Common finance datasets (accounting, budgets, reconciliations)
- Pitfalls of manual data handling
Data Wrangling Techniques
- Identifying messy data (duplicates, blanks, mismatched formats)
- Cleaning in Excel (remove duplicates, TRIM, VLOOKUP/XLOOKUP)
- Intro to Power Query
- Combining multiple datasets (ledger, invoices, transactions)
Structuring Data for Reporting
- Setting up rows, columns, relationships
- Proper headers, categories, validations
- Source data prep for pivot tables
- Basic pivot table usage (summaries, slicing, rearranging)
Using Excel & BI Tools
- Chart types (bar, line, waterfall)
- Conditional formatting
- Slicers and filters for interactivity
- Basics of Power BI (connecting to Excel, simple visuals)
- Exporting and formatting reports
Automating Routine Tasks
- Reusable queries and auto-refresh
- Template reports for recurring tasks
- Linking multiple sheets/tabs
- File hygiene (naming, version control, safety)
Good Data Habits & Governance
- How poor data affects accuracy and timelines
- Basics of data governance
- Role of frontline teams in clean, compliant records
- Collaborating with MIS/data teams
- Documentation (comment logs, change tracking, data logs)
2 Days
Dirty Money Decoded
- Money laundering basics, beyond the classic three stages
- How terrorist financing differs from money laundering (overlaps & unique traits)
- Proliferation finance: small legal transactions, big illegal operations
- Societal, financial, and geopolitical impacts
Frameworks & Global Cooperation
- FATF “40+9,” UN, Egmont Group, Wolfsberg Principles
- Regional bodies (APG, MENAFATF), sanctions, watchlists, and nonproliferation
Countering Terrorist Financing
- Legal vs. illegal funding sources
- Role of charities, donations, and unregulated value transfers
- FATF’s CFT focus and real-life extremist case snapshots
Identifying Red Flags & Industry Vulnerabilities
- Typologies: shell firms, tradebased, cyber laundering, charities
- Misuse of banking, insurance, capital markets, fintech
- Product-level risks: prepaid cards, crypto, NFTs, cross-border payments
Suspicious Behavior & Reporting
- Defining “suspicion” and spotting hidden triggers
- Internal reporting flow and the MLRO’s role (from review to SAR)
Risk-Based Approach (RBA) & KYC
- Applying RBA to high-risk industries, jurisdictions, PEPs
- CDD & EDD: onboarding to ongoing monitoring
- Beneficial ownership, complex structures, and audit trails
Transaction Monitoring & Screening
- Designing effective monitoring, dealing with thresholds and false positives
- Sanctions screening: name matching vs. intent
Governance & Accountability
- Embedding AML into corporate culture (Board, MLRO, compliance)
- Preventing misconduct through good governance
- Common oversight failures and their repercussions
2 Days
Forensics 101
- Forensic investigation vs. audit vs. compliance
- Real-world examples: Embezzlement, procurement fraud, vendor schemes
- The mindset of an investigator: scepticism, structure, and objectivity
Red Flags and Fraud Risk
- Fraud elements classifications (triangle, diamond, pentagon)
- Common types of financial fraud
- New-age financial frauds.
- Behavioural red flags and organisational blind spots
- Key financial indicators of manipulation or concealment
Investigation Process
- Investigation approaches
- From allegation to action: planning the investigation
- Understanding the “triage” phase – what to prioritise
- Defining scope
Evidence Gathering – Financial, Digital, and Physical
- Sources of evidence: books, emails, logs, voice notes, CCTV, etc.
- Mapping evidence
- Preservation and chain of custody
- Digital forensics basics
Interviewing Skills for Effective Questioning
- How to plan and conduct investigative interviews
- Asking the right questions
- Reading behavioural cues
- Do’s and don’ts of interviewing
Transaction Tracing
- Basics of financial statement analysis
- Forensic accounting techniques for tracing fund diversions and misappropriations
- Understanding and tracing bank records, shell entities, and fake invoicing patterns
- Effective use of technology
Collaboration – Working with Authorities
- Importance of other industry experts
- Interfacing with law enforcement and regulators
- Effective communication with stakeholders
Documentation & Report Writing
- Writing clear, defensible forensic reports
- Presentation using visual tools like charts, timelines, and maps.
- Making reports court-ready without legal jargon
2 Days
Financial Transactions & Fraud Schemes
- Basic Accounting & Auditing Theory
- Common Fraud Schemes (e.g., asset misappropriation, corruption, financial statement fraud)
- Internal Controls & Red Flag Detection
- Analysing financial transactions
Investigation & Evidence Gathering
- Stages of investigation: Planning to Reporting
- Fraud Investigation Techniques
- Interviewing
- Tracing Illicit Transactions and Data analysis
- Sources of Information & Public Records Research
Law & Legal Frameworks
- Criminal vs. Civil Law in fraud cases
- Rules of Evidence & maintaining Chain of Custody
- Testifying as an Expert Witness & courtroom procedures
- Legal rights
Fraud Prevention & Deterrence
- Crime Causation & White-Collar Crime Dynamics
- Occupational Fraud & building antifraud controls
- Fraud Risk Assessments & implementing proactive measures
- ACFE Code of Professional Ethics & professional standards
2 Days
Introduction & Overview
- CISA Exam Structure & Requirements
- Key Resources (ISACA Manual, QAE Database)
- Training Objectives & Approach
Information Systems Auditing Process
- IS Audit Standards & Frameworks
- Risk‐Based Audit Planning & Resource Allocation
- Audit Project Management, Internal Controls & Control Testing
- Reporting & Communication
Governance & Management of IT
- IT Governance Frameworks (COBIT, ISO)
- IT Strategy & Alignment (KPIs, Balanced Scorecards)
- Risk Management & Compliance (SOX, GDPR)
- Policy Development & Oversight
Information Systems Acquisition, Development & Implementation
- Project Management & Governance (Waterfall, Agile)
- Systems Development Life Cycle (SDLC)
- Acquisition & Vendor Management (RFPs, SLAs)
- Quality Assurance & Testing
IT Service Management & Monitoring
- ITIL Concepts (Incident, Problem, Change)
- Job Scheduling & Performance Tuning
- Automated Monitoring & Alert Systems
Business Resilience Fundamentals
- Key Concepts: RTO, RPO, Business Impact Analysis
- Foundations of Crisis Management
Business Continuity & Disaster Recovery
- Developing & Testing BCP/DRP
- Hot, Warm, Cold Sites & Tabletop Exercises
- Maintenance & Continuous Improvement
Incident Response & Crisis Communications
- IR Teams, Roles & Escalation
- Stakeholder & Media Communication
- Coordinating with Regulators & Law Enforcement
Protection of Information Assets (Foundations)
- Information Security Concepts (CIA Triad)
- Access Controls & Identity Management (RBAC, MFA)
Protection of Information Assets (Advanced)
- Network Security & Encryption (Firewall, IDS/IPS)
- Physical & Environmental Security
Threat & Vulnerability Management
- Penetration Testing & Vulnerability Assessments
- Emerging Threats (Ransomware, Social Engineering, IoT)
Data Protection & Privacy
- GDPR, CCPA, HIPAA
- Data Classification, Retention & Destruction
Wrap‐Up & Exam Prep
- Mock Questions & Key Exam Tips
- Final Q&A & Next Steps
Your Mentors
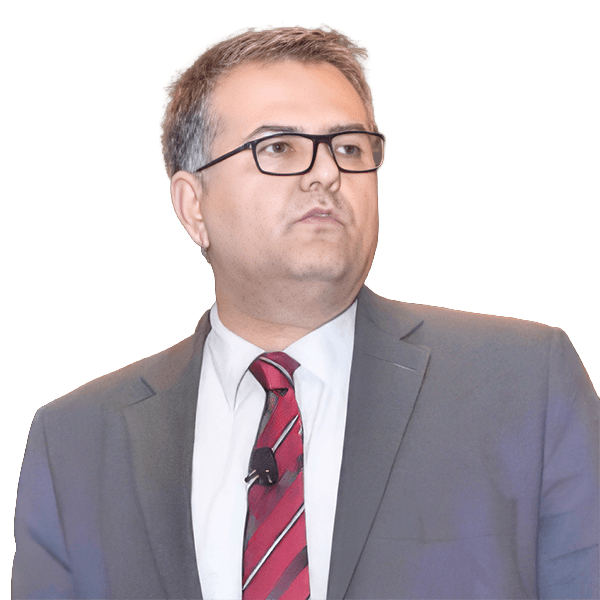
ANAND PRAKASH JANGID is a Chartered Accountant and Certified Information System Auditor specializing in risk and fraud analytics, machine learning, and blockchain.
He has worked with Goldman Sachs, conducting audits across various geographies and functions, including forex audit, DP audits, anti-money laundering, Basel II, business continuity planning, and operational risk. Prior to Goldman Sachs, Anand was with Infosys Technologies Limited, developing regulatory compliance frameworks like the Sarbanes-Oxley Act and contributing to the BASEL II Accord implementation.
He has implemented Enterprise Risk Management and IT audit for international projects in the USA, UK, Japan, China, and more. Anand is a visiting faculty at IIM Bangalore, National Forensic Science University, and BML Munjal University, and a sought-after speaker at ISACA conferences. He also serves as an expert member on committees of IRDAI, ICAI, and ISACA.
Anand Prakash Jangid
Information System & Cyber Security Audit
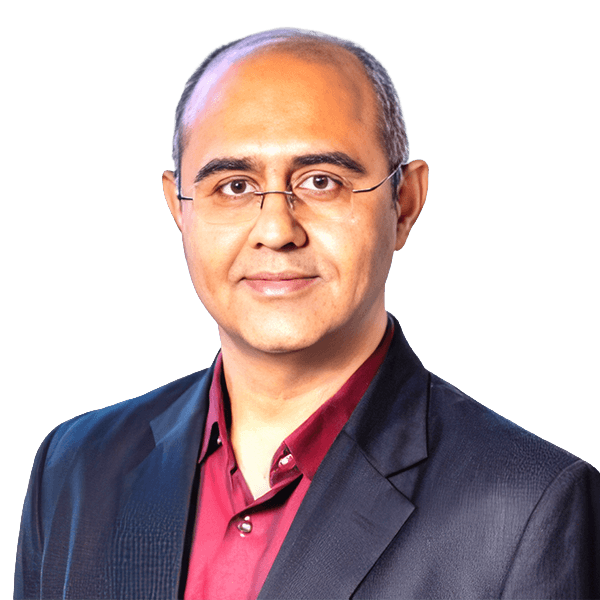
DR. DURGESH PANDEY, PhD (Forensic Accounting), is a Chartered Accountant, Law Graduate, Certified Fraud Examiner (ACFE–USA) and Honorary Professor at the University of Portsmouth, UK. With 15+ years of experience, he has led 200+ financial crime and money laundering investigations, and has worked with the Enforcement Directorate, Economic Offence Wing and Anti-Corruption Bureau in India.
He is the author of Forensic Foresights – Case Based Perspective on Forensic Accounting Standards (Taxmann), prescribed as a textbook by leading universities and professional institutions. He has published widely on financial crime and AML/CFT and serves on editorial boards of acclaimed academic Journals.
Dr. Pandey has trained more than 25,000 professionals in workshop settings, including Chartered Accountants, bankers and corporate executives. He has conducted specialised AML/CFT and financial crime training for police and enforcement officials across 35+ countries, including programs at Naif Arab University for Security Sciences, Saudi Arabia. He has also advised large corporates in project bidding with FIU India on AML/CFT initiatives.
As a member of the Expert Group developing Forensic Accounting and Investigation Standards (FAIS), he advises corporates and regulators on AI-driven approaches to financial crime detection and investigation.